Ever-expanding regulatory requirements (without matching resources)
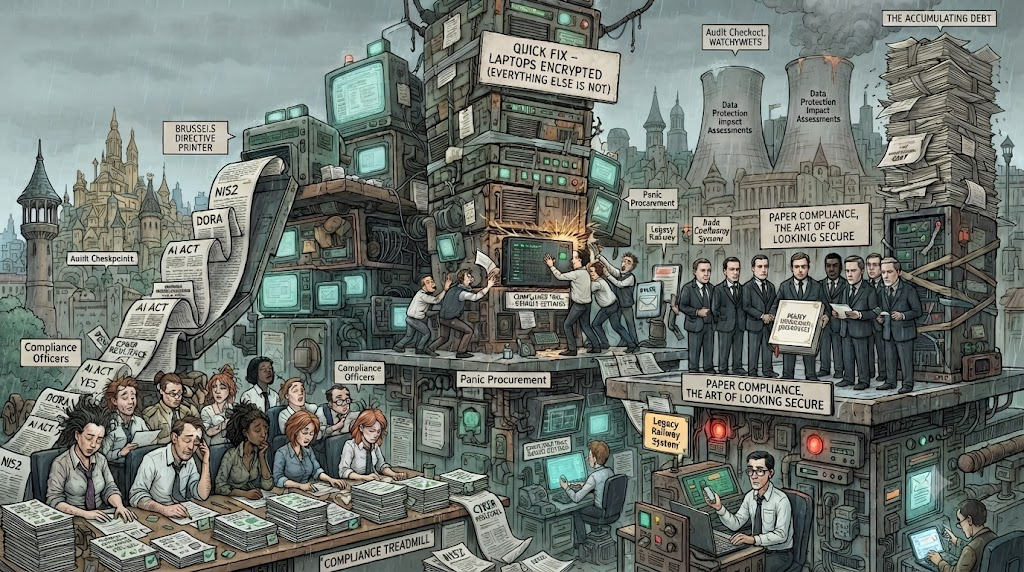
Europe’s regulatory machinery has developed a remarkable talent for producing rules at a pace that would make a rabbit colony blush, while steadfastly refusing to provide the carrots required to implement any of it. NIS2, DORA, the AI Act and the Cyber Resilience Act all arrive with noble intentions, serious faces, and a level of resourcing that could generously be described as fictional. An organisation can stumble from one deadline to the next while quietly constructing a towering pile of security debt that threatens to wobble, topple, and flatten anyone foolish enough to look directly at it.
The clerk’s brief
From the clerks, for the Patrician’s eyes
Compiled September 2026. Entries run newest first. Observations that have stopped being news but not stopped being true are absorbed into the procession at the end. His Lordship is reminded, respectfully, that every deadline below was set by people who will not be implementing it.
September 2026: The platform arrives on the day, in its first stage
On 11 September 2026 the Cyber Resilience Act’s reporting obligations applied, and ENISA deployed the initial operating capability of the Single Reporting Platform the same day, with its functions to be expanded over the coming months. The clerks note that the obligation arrived complete and the platform arrived in instalments.
July 2026: The Omnibus on AI becomes law
The Digital Omnibus on AI, proposed beside the Digital Omnibus on 19 November 2025, was signed on 8 July 2026, published in the Official Journal on 24 July as Regulation (EU) 2026/1744 and in force from 27 July. It moved the AI Act’s high-risk obligations for the listed standalone uses from 2 August 2026 to 2 December 2027, and those for systems inside products already regulated for safety from 2 August 2027 to 2 August 2028. Recital 40 gives two reasons: standards not yet available, and national authorities not yet established. On the Commission’s own list, updated 7 September 2026, six member states had still not named a market surveillance authority, thirteen months after the deadline for doing so. The clerks note that one reason the Regulation gives for postponing the rule is that the authorities who were to enforce it had not yet been established, and that the postponement itself was enacted on time.
July 2026: Four member states go to court over NIS2
On 8 July 2026 the Commission referred Ireland, Spain, France and the Netherlands to the Court of Justice for failing to transpose NIS2, and asked for a lump sum and daily penalties. The clerks note that the directive’s first rewrite had been proposed six months earlier, while four member states had yet to write the original into law.
July 2026: The Cyber Resilience Act’s clock is set for September
From 11 September 2026, manufacturers of products with digital elements are required to report actively exploited vulnerabilities: an early warning within 24 hours of becoming aware, and a full notification within 72. ENISA’s Single Reporting Platform, through which all of this is meant to flow, is officially scheduled to be operational by that same date; as of late June 2026 it was not yet live. The clerks observe that the obligation and the infrastructure for meeting it are currently timetabled to arrive on the same day, an arrangement whose elegance they admire and whose prudence they decline to assess.
February 2026: The data protection authorities draw a line
On 10 February 2026 the EDPB and EDPS adopted a joint opinion on the Digital Omnibus, welcoming the parts that reduce reporting burden, notably a higher risk threshold and a longer deadline for notifying personal data breaches, and strongly urging the co-legislators to reject the proposed narrowing of the definition of personal data as going clearly beyond the court’s jurisprudence. The clerks expect the argument to run through 2026, and privately expect to enjoy it.
January 2026: NIS2 receives its first rewrite
On 20 January 2026 the Commission proposed targeted amendments to NIS2, to simplify compliance, align the directive with the Cybersecurity Act, and connect it to the single entry point for incident reporting proposed in the Digital Omnibus. The directive is barely a year into enforcement and already being simplified. The clerks decline to call this failure. They note only that the machinery has begun regulating its own regulations, which is either maturity or recursion, and that from below the treadmill the two are difficult to tell apart.
November 2025: The Omnibus arrives, and finance gets its list
On 19 November 2025 the Commission adopted the Digital Omnibus proposal, amending a large corpus of digital legislation at a stroke, with a single entry point for incident reporting across NIS2, GDPR, DORA and the Critical Entities Resilience Directive. The day before, on 18 November 2025, the European supervisory authorities named the first 19 critical ICT third-party providers, bringing them under direct financial-sector oversight, and the designation is filed under lock-in. In the same week, Europe resolved to watch its suppliers more closely and to paper its own entities less. The clerks note that both could even be right.
The procession, with dates
The arc now repeats often enough to be told with dates. A directive is adopted. A transposition deadline passes with most member states absent, as NIS2’s did in October 2024. Guidance fogs, enforcement begins against the states themselves before any entity, as from November 2024, with reasoned opinions to 19 member states in May 2025 naming Germany, France, Spain and the Netherlands, and within roughly a year the simplification proposals arrive, as they did in November 2025 and January 2026. The older strata carry on underneath: GDPR, applicable since May 2018 and still unevenly implemented, would itself be amended by the same Omnibus proposal that adds the new reporting plumbing.
The Union has begun building infrastructure rather than only paperwork: ENISA’s European Vulnerability Database has been live since May 2025, and in April 2025 DORA produced the first registers of who in European finance depends on whom. The resourcing gap has not closed. It has been promoted: it is now the subject of legislation, rather than merely its victim.